Last Updated: 14th October 2026
SaaS GRC that keeps you audit-ready, not audit-scrambling
SOC 2. ISO 27001. PCI DSS. One cloud-based platform, with evidence collected automatically, always audit-ready.
Anyone at a SaaS company who has been through a SOC 2 or ISO 27001 audit knows how it goes: a shared spreadsheet, a scramble for evidence, and engineers pulled off product work. The same cost comes back with the next audit if the evidence has gone stale in between.
The 51 future-dated requirements in PCI DSS v4.x have applied since 31 March 2025, so assessments of SaaS companies in PCI DSS scope now include them.
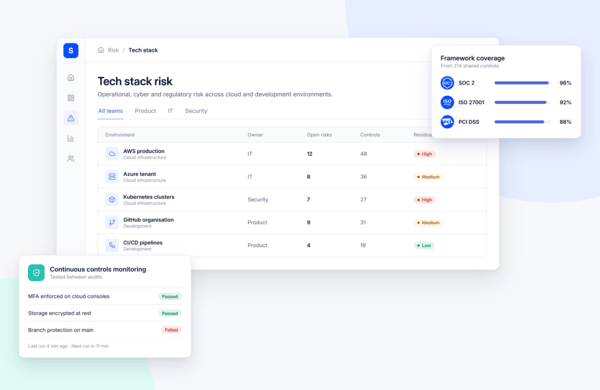
SureCloud's continuous controls monitoring (CCM) reduces audit prep time by 75%. Evidence collects continuously, so it's on file before the auditor asks and builds up between audits.
The GRC team that's ready before you hire one
A senior GRC hire costs £73k on average in the UK, and most SaaS teams would rather put that into product. Gracie AI, the virtual GRC team, takes on the audit-readiness work that hire would do: mapping controls, chasing evidence, flagging gaps.
Your engineers keep working on the roadmap while Gracie handles the audit groundwork. Gracie doesn't replace your people. AI operates the role. Humans lead the programme.
Gracie AI Agents with Personas and Skills work in defined roles. Each Persona sets an agent's role and authority, such as a Risk SME or Compliance SME, and Skills codify the steps and standards for each activity. Read how SureCloud launched Gracie AI as a virtual GRC team.
Control Risk Across Your Entire Tech Stack
As your technology footprint grows, so does your risk. SureCloud maps and manages operational, cyber and regulatory risk across cloud infrastructure and development environments, and gives product, IT and security teams one view of risks and mitigations. The same controls support SOC 2, ISO 27001 and PCI DSS, and continuous controls monitoring keeps them tested between audits.
SaaS GRC vs. legacy enterprise GRC
|
Typical GRC platforms |
SureCloud |
|
|
What it does with risk |
Reports on risk. Shows it. |
Acts on risk. Reduces and mitigates it. |
|
Architecture |
Siloed point solutions |
One connected platform across every GRC domain |
|
AI |
AI retrofitted onto legacy architecture |
Built for AI from day one (AI-first). Gracie AI is the virtual GRC team |
|
Evidence |
Static, point-in-time snapshots |
Event-sourced, tracks change over time. Continuous controls monitoring |
|
Time to value |
Varies by platform and configuration |
Assure can go live as fast as one week. QuickStart usually takes four to eight weeks on Automate and Orchestrate |
7 CCM Platforms Compared: Find Issues Before Auditors Do compares the CCM market, and the ISO 27001 vs SOC 2 decision framework helps you choose a framework first.
Built for how your team actually scales
SaaS GRC buyers usually start for one of two reasons: a first audit or several frameworks at once. Assure suits the first; Automate and Orchestrate suit the second.
Head of Security or CISO
You need a clear audit position without pulling engineers off the roadmap. SureCloud keeps controls mapped and evidence current, so answering an auditor takes a short review.
Read more about the benefit of SureCloud for CISO's
GRC manager
Compliance lead or vCISO
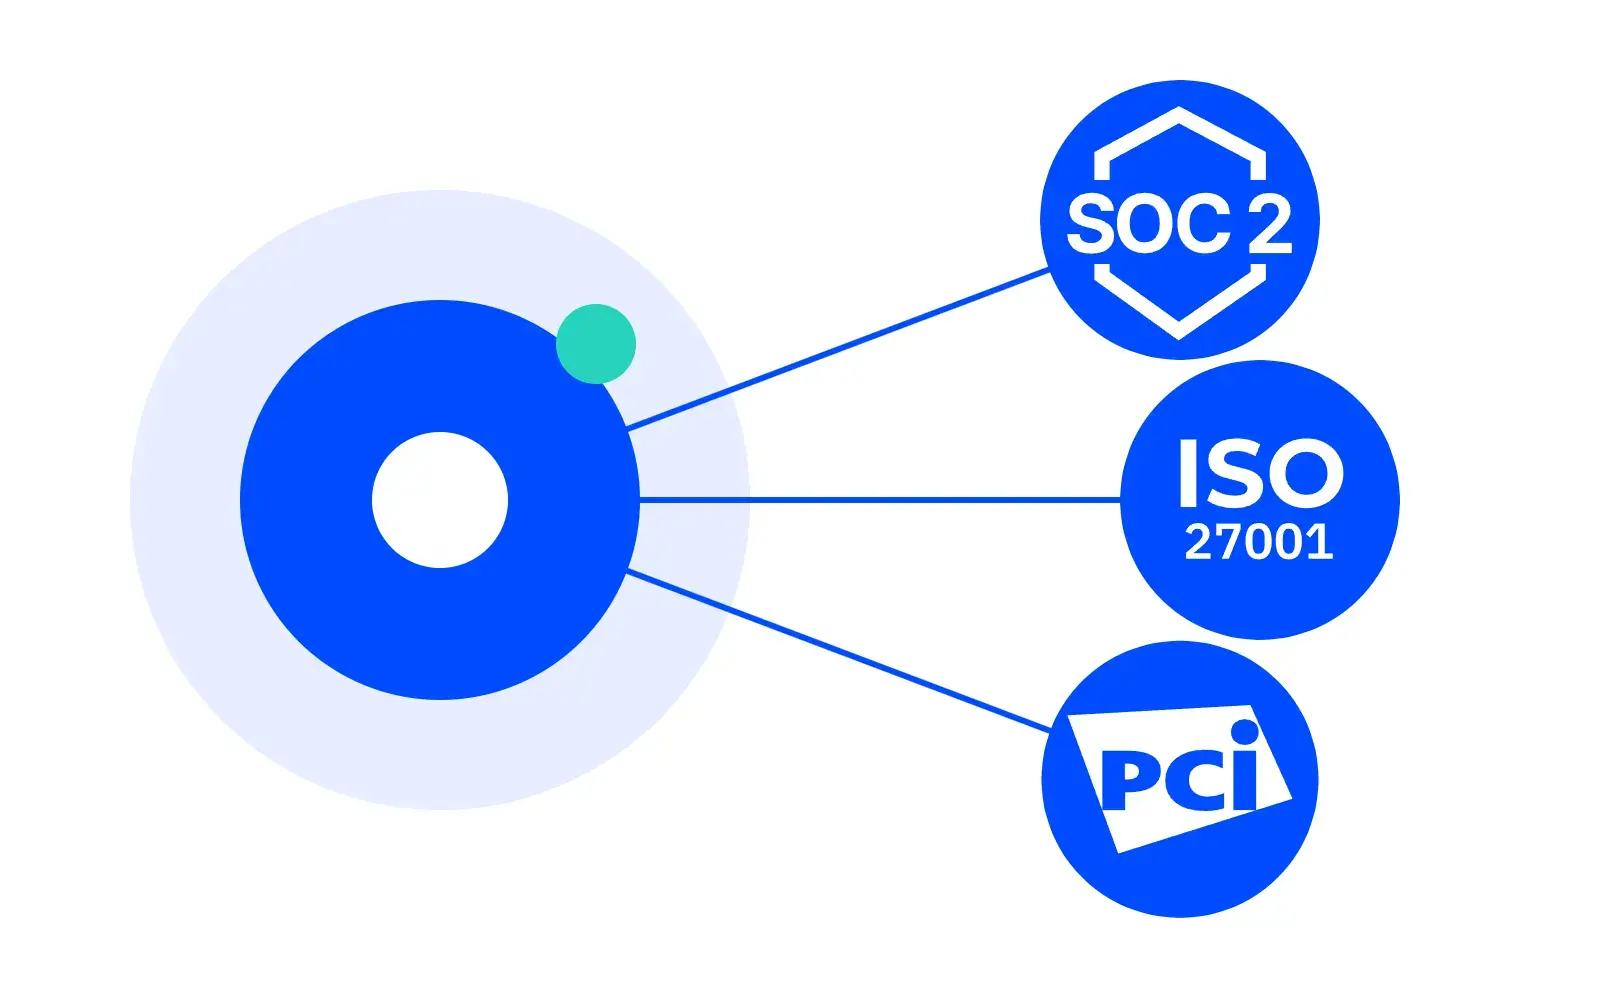
You map each control once and reuse it across SOC 2, ISO 27001 and PCI DSS.
Read more about the benefit of SureCloud for Compliance Managers
Mid-market and first audit
Enterprise and multi-framework
Managing SOC 2, ISO 27001 and PCI DSS at once, across multiple products? One platform and one control library mean you collect evidence once and map it across audits.
Future-Proof Compliance Without Slowing Down
SOC 2, ISO 27001 and PCI DSS each add control requirements, and every new framework a customer asks for adds more. EU NIS2 covers medium-sized and large entities in 18 critical sectors, so SaaS companies with EU customers should check whether their services fall in scope. SureCloud reduces manual work with automated workflows and reporting by framework, from one cloud-based GRC platform.
The three frameworks come from different bodies, so each is evidenced and assessed in its own way. A SOC 2 report is issued by a CPA firm under the AICPA's SOC suite of services. ISO 27001 certification comes from a certification body, and ISO notes that an accredited body may add a further layer of confidence. PCI DSS, maintained by the PCI Security Standards Council, applies when you store, process or transmit cardholder data, or can affect the security of the cardholder data environment.
SureCloud maps your controls across all three, so adding a framework extends the programme from controls you're already running. Why SOC 2 Needs a New Approach in 2026 is worth reading before your next audit cycle.
The Risk Reckoning is here.
SureCloud's Risk Reckoning 2025 research surveyed nearly 200 UK executives and leaders. Among enterprises, it shows how prepared they feel and how fragmented their tooling is.
- 87% of UK enterprise executives say they're prepared for a major GRC event.
- 45% of UK enterprises have integrated platforms.
- 62% of UK enterprises use four or more GRC tools.
Most enterprise executives feel prepared, yet fewer than half of enterprises run an integrated platform.
Download the Risk Reckoning white paper for the full findings.
Plans that scale with your business
SureCloud's SaaS GRC solutions come in three plans. Each scales into the next, and your configuration, data and history carry across.
Pricing is based on your requirements and the plan and products you need.
Assure: Risk & Compliance on Autopilot
The first-certification answer for organisations focused primarily on compliance certifications. The package includes 10 named users, ISO 27001 and SOC 2 content packs, a control library, evidence templates, risk registers, CCM (Basic), a Trust Centre and Gracie Basic.
Automate: From Spreadsheets to AI-Assisted Workflows.
Orchestrate: Intelligent GRC for the Enterprise.
Resources for SaaS security and compliance teams
Guides for preparing your next audit, whether it's SOC 2, ISO 27001 or continuous compliance.
- SOC 2 for Startups: When to Start, Cost and Readiness
- ISO 27001 vs SOC 2 for Enterprise: A Decision Framework
- Why SOC 2 Needs a New Approach in 2026
- 7 CCM Platforms Compared: Find Issues Before Auditors Do
- SOC 2 Compliance Checklist: 8-Phase Audit Readiness Guide
- Agentic AI Controls Monitoring: What It Can and Can't Do
FAQ’s
What is SaaS GRC?
SaaS GRC is governance, risk and compliance software built for software companies. It maps your controls once and keeps evidence current across frameworks like SOC 2, ISO 27001 and PCI DSS, so each certification draws on the same work. SureCloud delivers it as a cloud-based platform.
Do I need SOC 2 or ISO 27001 first?
It depends on your buyers. SOC 2 is the default ask from US enterprise customers, and ISO 27001 from European and public-sector ones. Check which framework your largest prospects name in security reviews, then read the ISO 27001 vs SOC 2 decision framework for the full comparison.
How is SureCloud different from Archer, SAP, or ServiceNow GRC for a SaaS company?
As a SaaS GRC vendor, SureCloud acts on risk where typical platforms stop at reporting it. It's one connected platform, built for AI from day one, with Gracie AI as the virtual GRC team. Assure can go live in as fast as one week, and QuickStart usually takes four to eight weeks on Automate and Orchestrate.
What does a GRC platform do for a mid-market SaaS company vs. an enterprise one?
A mid-market team usually wants its first SOC 2 or ISO 27001 audit evidenced quickly, often without a dedicated compliance hire. An enterprise team runs several frameworks across multiple products and needs one control library, so evidence is collected once and reused across audits.
Continuous controls monitoring reduces audit prep time by 75%. Gracie AI Agents with Personas and Skills handle the groundwork a GRC hire would, so your next SOC 2 or ISO 27001 audit is a non-event.
4.5 out of 5
"Excellent support team"We've been happy with the product and the support and communication has been excellent throughout the migration and onboarding process.
Posted on
G2 - SureCloud
5 out of 5
"Great customer support"
The SureCloud team can't do enough to ensure that the software meets our organisation's requirements.
Posted on
G2 - SureCloud
4.5 out of 5
"Solid core product with friendly support team"
We use SureCloud for Risk Management and Control Compliance. The core product is strong, especially in validating data as it is...
Posted on
G2 - SureCloud
5 out of 5
"Excellent GRC tooling and professional service"
We've been happy with the product and the support and communication has been excellent throughout the migration and onboarding process.
Posted on
G2 - SureCloud
4.5 out of 5
"Straightforward Implementation, Intuitive Use, and Brilliant Support"
SureCloud has been straightforward to implement and tailor to our framework. It’s intuitive to use, so our teams have adopted it quickly...
Posted on
G2 - SureCloud
5 out of 5
"Easy to Use, Beautiful Graphs, and a Helpful, Responsive Team"
Very easy to use and really nice graphs are created. The team are also very helpful and quick to respond
Posted on
G2 - SureCloud