gartner-reviews-dark 4.2/5 (56)

Last Updated: 20th October 2026

GRC for energy and utilities, built for NIS2

Operational resilience for organisations that can't afford to fail.

NIS2 has extended its reach across critical infrastructure.

Large energy and water operators are essential entities under NIS2, the EU's updated network and information security directive. Member States must set maximum fines for essential entities of at least €10M or 2% of global turnover, whichever is higher, for breaches of the security or incident reporting rules. Management bodies can be held liable for infringements. SureCloud provides Governance, Risk and Compliance for Energy and Utilities: a NIS2 compliance platform for critical infrastructure, so you can meet these obligations and prove it.

hero-vert-critical-infractructure-1
48% of breaches now involve a third party.
50% Almost half of NIS2 organisations rank supply chain attacks as a top concern.”
NIS2 isn't on the horizon.
It's already here.

NIS2 full compliance deadline: October 2026.

Supply chain risk is now a legal obligation.

tile-nis2

NIS2

NIS2 covers energy, water, transport, digital infrastructure and more. Member States had to apply it from 18 October 2024, and registration and enforcement now run country by country, so your obligations depend on where you operate. Large operators in high-criticality sectors such as energy and water are essential entities, and medium-sized operators in those sectors are important entities. Essential entities face maximum fines of at least €10M or 2% of global turnover, and important entities €7M or 1.4%, whichever is higher in each case, for breaches of the security or incident reporting rules (Article 34). 
tile-expanding-scope

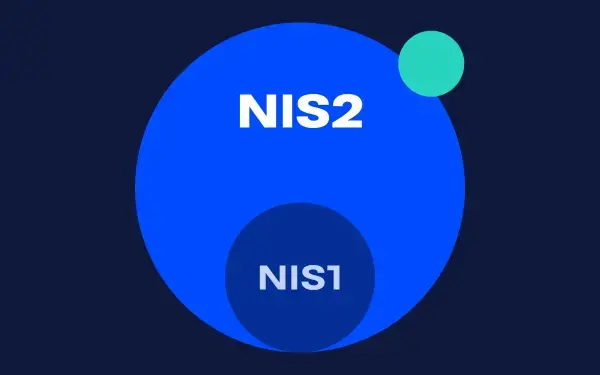
Expanding scope

NIS2 reaches more sectors and more organisations than NIS1. Management bodies must approve and oversee your cybersecurity risk-management measures and can be held liable for infringements of those measures (Article 20). Supply chain security is one of those measures, so your direct suppliers and service providers belong in your risk programme as well as your own operations (Article 21(2)(d)). 
tile-uk-bill

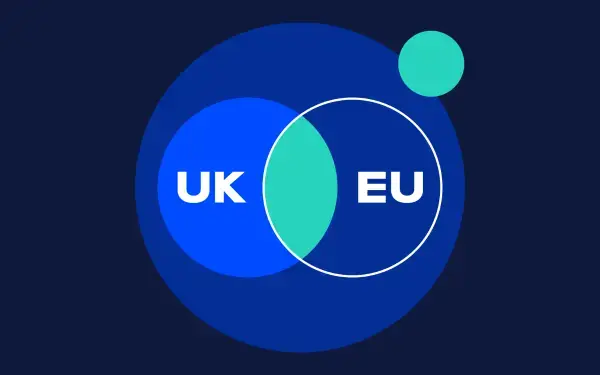
The UK Cyber Security and Resilience Bill

The Cyber Security and Resilience Bill is before the House of Lords and would amend the NIS Regulations 2018, with broader scope and tighter incident reporting for UK-regulated organisations. UK operators regulated under those Regulations already assess themselves against the NCSC Cyber Assessment Framework, and the NCSC published CAF v4.0 in August 2025. NIS2 applies where you operate in the EU, so UK groups with EU operations can answer to both regimes. Our explainer on the Bill sets out what's changing. 
tile-energy-operators

What energy and utilities operators face

Energy and utilities operators run legacy infrastructure alongside new digital technology, and grid resilience depends on both. Operational technology in substations and generation can be hard to take offline for patching, and contractors and equipment vendors sit inside the supply chain that NIS2 holds you accountable for. A risk and compliance solution for energy works best when it holds that whole mix in one place.

The Energy sector cyber security strategy, published in May 2026 by DESNZ, the NCSC, NESO and Ofgem, sets out what the government will do to protect Great Britain's energy system and consumers. We've unpacked what the strategy means for operators and what energy sector breaches now cost.
From compliance documentation to compliance evidence.

feature-nis2-native-compliance

NIS2-native compliance:

Controls, evidence templates, and reporting aligned to NIS2 requirements. Map once; stay compliant as the standard evolves.
feature-third-party-risk

Third-party risk management:

Supply chain risk is a NIS2 legal obligation. SureCloud's third-party risk management software assesses, scores, and monitors every vendor in scope, at scale. 
feature-incident-management

Incident management:

NIS2 mandates incident reporting within defined timelines. SureCloud logs, tracks, and reports incidents with the documentation regulators require.
feature-business-continuity

Business continuity:

Operational resilience planning connected to live risk data. Tabletop exercises, impact analysis, and response plans aligned to NIS2 and ISO 22301.
feature-continuous-control-monitoring

Continuous control monitoring:

Ongoing automated control testing. Failures surface as they happen, between audits. 
blue-timer
50-70% reduction in enterprise-wide risk reporting effort
blue-timer
50% faster third-party risk assessments
blue-timer
40% faster decision-making

How long does implementation take, and what does it cost?

Energy and utilities teams often ask two things early: how long implementation takes and what it costs. The answers depend on which plan fits your estate.

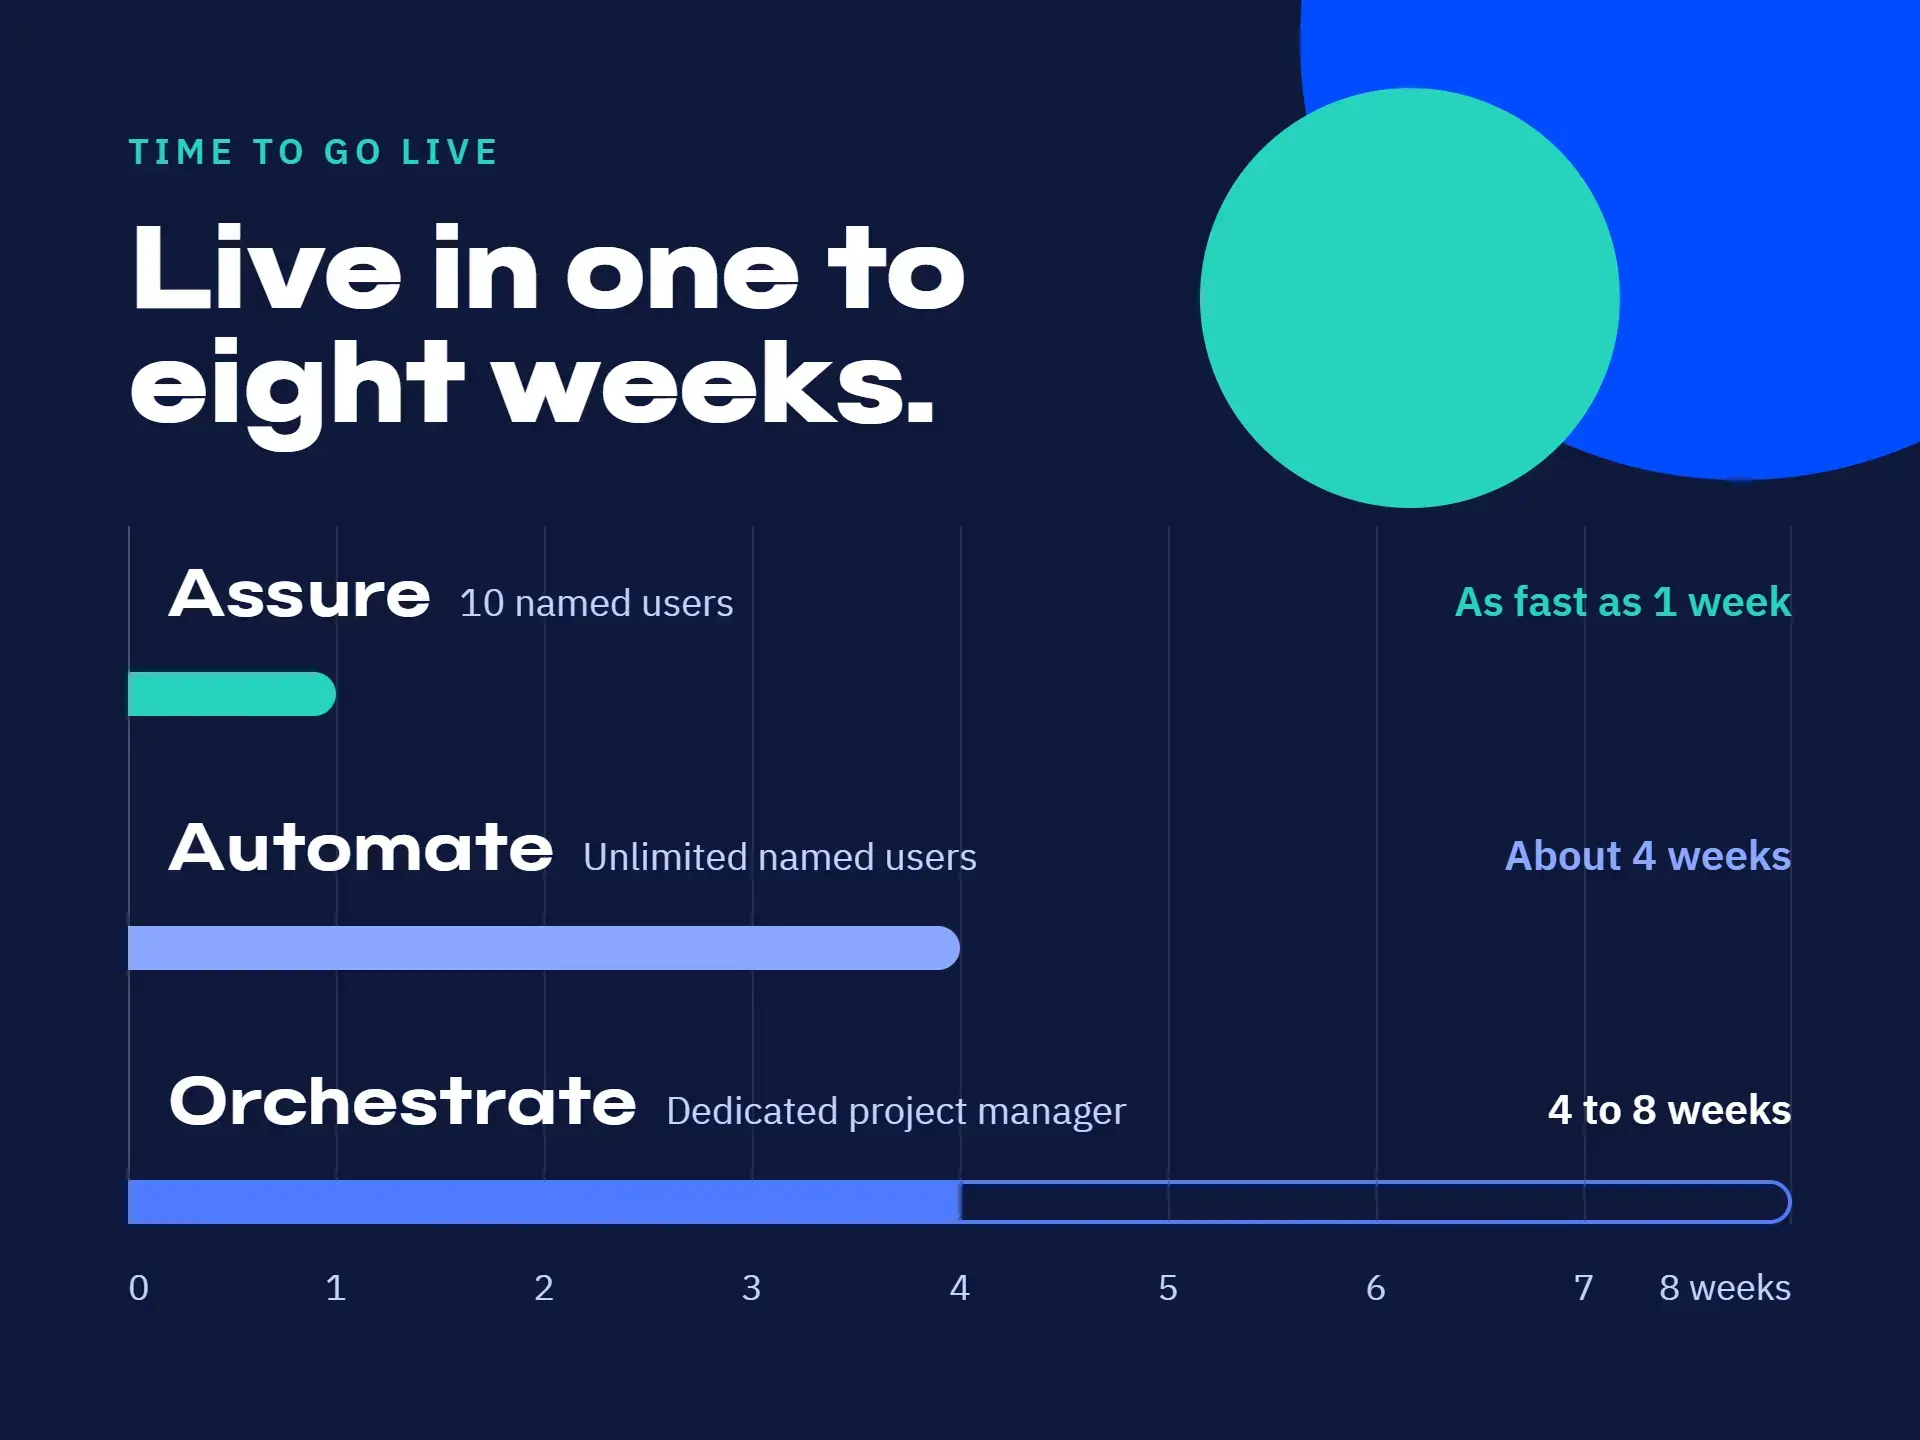
Assure suits operators starting a NIS2 programme without dedicated GRC staff. It's a fixed package with 10 named users, and it can go live as fast as one week.

Automate suits operators who run NIS2 controls and supplier risk together. You pick two base products from third-party risk, risk or compliance, named users are unlimited, and QuickStart takes about four weeks.

Orchestrate suits larger estates that run several GRC domains at scale. Named users are unlimited, a dedicated project manager leads the implementation, and enterprise programmes take four to eight weeks.

Pricing follows your programme, including your team size, the tools you already run and your compliance objectives. Request pricing and the team will send the pricing guide, then scope a plan to your estate.

implementation-timeline-2b (1) (1)

 SureCloud's solution makes IRAM2-compliant risk management easy by drastically simplifying the implementation of the methodology. — UK Water Provider.

SureCloud hosts our key data privacy processes. It has streamlined these processes, making privacy risk management easier and contributing towards our overall compliance with data protection law and best practice. — Independent body in association with the UK Department of Education

Easy to use, beautiful graphs and a helpful, responsive team. — UK Public Sector


gartnerdark forrester_logo idc-logo vertandix gigaom-logo-dark qks

Common Questions from Energy and Utilities Teams

How long does it take to implement a GRC platform for a critical infrastructure or energy business?

QuickStart, SureCloud's structured implementation, usually takes about four weeks, and four to eight weeks for larger estates. Assure can go live as fast as one week. Gracie AI Agents with Personas and Skills draft the configuration for admin approval, and the platform supports NIS2 and NCSC CAF v4.0. See how Gracie AI configures compliance in minutes. 

How is SureCloud priced for NIS2 and NCSC CAF compliance?

Pricing follows your compliance objectives, the size of your team and the tools you've already got. Automate and Orchestrate include unlimited named users, and Assure includes 10. Request pricing and the team will send the pricing guide, then scope a plan to your estate. 

Is SureCloud a good fit for NIS2 and NCSC CAF compliance in a critical infrastructure and government firm?

Yes. SureCloud runs NIS2 and NCSC CAF v4.0 in one platform, so a team maps each control once and evidences it against both frameworks. SureCloud is built for operators who run both frameworks as ongoing programmes. Our guide to NIS2 and NCSC CAF v4.0 compliance covers where the two overlap.

Does SureCloud cover third-party and supply chain risk under NIS2?

Yes. NIS2 lists supply chain security among the measures management must oversee (Article 21(2)(d)), and SureCloud's third-party risk management, available on Automate and Orchestrate, runs alongside your core NIS2 controls. It assesses, scores and monitors every vendor in scope, so you've got current evidence for each, and customers complete third-party risk assessments 50% faster. See SureCloud third-party risk management software. 

We're still running compliance on spreadsheets. What are we missing under NIS2?

Spreadsheets record a point in time, and supervisors of essential entities can request evidence of how your measures are implemented (Article 32). A platform keeps control status current and links evidence to each control as the work happens, so you're answering from live records. See the three gaps spreadsheets miss under NIS2. 

How does SureCloud map NIS2 to NCSC CAF v4.0?

Our mapping article finds that CAF v4.0 already covers much of NIS2 Article 21, and it names three remaining gaps: incident reporting timelines, supply chain depth and board-level accountability. In the platform, you test a control once and its evidence maps across both frameworks. See the full NIS2 to CAF v4.0 mapping. 

g2-orange
Reviews

Read Our G2 Reviews

Review us on G2

4.5 out of 5

"Excellent support team"We've been happy with the product and the support and communication has been excellent throughout the migration and onboarding process.

Posted on
G2 - SureCloud

5 out of 5

"Great customer support"

 The SureCloud team can't do enough to ensure that the software meets our organisation's requirements. 

Posted on
G2 - SureCloud

4.5 out of 5

 "Solid core product with friendly support team"

 We use SureCloud for Risk Management and Control Compliance. The core product is strong, especially in validating data as it is... 

Posted on
G2 - SureCloud

5 out of 5

 "Excellent GRC tooling and professional service"

We've been happy with the product and the support and communication has been excellent throughout the migration and onboarding process.

Posted on
G2 - SureCloud

4.5 out of 5

"Straightforward Implementation, Intuitive Use, and Brilliant Support"

SureCloud has been straightforward to implement and tailor to our framework. It’s intuitive to use, so our teams have adopted it quickly...

Posted on
G2 - SureCloud

5 out of 5

"Easy to Use, Beautiful Graphs, and a Helpful, Responsive Team"
Very easy to use and really nice graphs are created. The team are also very helpful and quick to respond

Posted on
G2 - SureCloud

NIS2 is live. Prove your resilience. Your Business Assured.