gartner-reviews-dark 4.2/5 (56)

Last Updated: 14th October 2026

Financial services risk management.

Built for a time when it matters most.

DORA enforcement is active. FCA fines are already issued. The window to demonstrate compliance, not just document it, is now. SureCloud gives financial services firms the platform to stay ahead of regulatory obligation and prove it. 
GRC Software For Financial Services
£16.1m in FCA fines already issued in Q1 2026. DORA Register of Information submissions were due March 2026. Enforcement is underway.
The regulatory clock isn't waiting

Supervisors increasingly ask for evidence. Financial services risk management depends on live control results, current vendor registers and board reports that show today's position. Financial services GRC software gives risk, compliance and audit teams one place to hold that evidence, and SureCloud's GRC platform for financial services links it to the DORA, FCA and Provision 29 obligations that depend on it.
tile-verts-fs-01 (1)

DORA

ICT risk management, incident reporting, and third-party oversight are live requirements. NCAs are deploying automated tools to cross-reference ICT registers. Late or inconsistent filings trigger enforcement automatically. Management are personally liable.
tile-verts-fs-02 (1)

FCA Operational Resilience

Firms must now evidence compliance with operational resilience rules, not just document it. Critical Third Party designations are expected in 2026. Third-party outsourcing registers and incident reporting final rules are incoming.
tile-verts-fs-03 (1)

UK Corporate Governance Code, Provision 29

From financial years beginning January 2026, boards must declare whether internal controls operated effectively and disclose any weaknesses. Boards must stand behind the control framework.
DORA vs. FCA Operational Resilience vs. Provision 29 at a glance

Framework

Applies to

Core requirement

Deadline or status

SureCloud coverage

DORA

EU-authorised financial entities (credit institutions, investment firms, insurers, payment institutions) and their ICT third-party providers. See Regulation (EU) 2022/2554.

Management bodies bear ultimate responsibility for ICT risk. Firms run an ICT risk framework, report major incidents, test resilience and oversee ICT providers.

Applicable since 17 January 2025. Firms maintain a Register of Information under Article 28(3) and submit it to their competent authority on its schedule; the Central Bank of Ireland window was 2 to 31 March 2026.

SureCloud's DORA framework brings ICT risk, third-party oversight, incident management, resilience testing and consolidated reporting together.

FCA Operational Resilience

Banks, building societies, PRA-designated investment firms, insurers, enhanced scope SM&CR firms, payment and e-money firms and others in the FCA's published scope.

Identify important business services, set impact tolerances and operate within them. Incident and third-party reporting rules add a reporting layer.

In force since 31 March 2022; transition ended 31 March 2025. PS26/2 reporting rules take effect 18 March 2027. HM Treasury announced the first four critical third parties on 10 July 2026; oversight began 13 July 2026.

SureCloud's Business Continuity & Resilience product, on the Automate and Orchestrate plans, holds continuity plans alongside business services and dependencies, runs scenario tests and tracks incidents.

UK Corporate Governance Code, Provision 29

Companies in the Code's listing categories (commercial companies and closed-ended investment funds). See the Financial Reporting Council's Code.

On a comply-or-explain basis, boards declare how effective the company's material internal controls have been.

Applies to financial years beginning on or after 1 January 2026.

SureCloud provides a central control inventory, automated workflows and dashboards for the evidence behind the declaration.

Third-party risk, evidenced not assumed

DORA Article 28 sets the rules for ICT third-party arrangements at EU-authorised firms, and the Prudential Regulation Authority's SS2/21 sets outsourcing and third-party expectations for the firms it regulates (updated March 2026, effective 18 March 2027). Groups with regulated entities in both the EU and the UK often find they're answering to both. SureCloud's guide to TPRM for financial services: FCA, DORA and SS2/21 shows how to keep one third-party record, using the DORA Register of Information format as the baseline and extending it with SS2/21 fields for non-ICT outsourcing. The guide also sets out what financial services third-party risk management (TPRM) software needs to support: a unified inventory, DORA Register exports, critical function classification, risk-proportionate due diligence workflows and concentration risk analysis.

SureCloud is recognised in the 2025 Gartner® Market Guide for Third-Party Risk Management Technology Solutions as a Representative Vendor.

SureCloud's third-party risk management holds the vendor library, tiering assessments, external vendor assessments and contract records in one platform, so there's a documented answer when a supervisor asks about a supplier. Third-party risk assessments run 50% faster on SureCloud.

From compliance documentation to compliance evidence.

The DORA in 2026: what banks, fintechs and insurers need guide explains what each firm type needs to evidence, and SureCloud's DORA framework page shows how the platform covers it. If you're preparing for Provision 29, start with the board controls checklist, and the FCA operational resilience guide sets out what supervisors expect firms to evidence.


What is DORA-native compliance?

SureCloud's DORA-native compliance maps third-party oversight, the Register of Information, incident reporting and ICT risk management to the requirements of Regulation (EU) 2022/2554 (DORA) out of the box.

From compliance documentation to compliance evidence.

sc2026_featuredora (1)

DORA-native compliance:

ICT risk management, incident reporting, Register of Information, and TPRM aligned to DORA requirements out of the box. SureCloud brings these DORA requirements together in one platform, with consolidated reporting across them.
sc2026_featurepassrate (1)

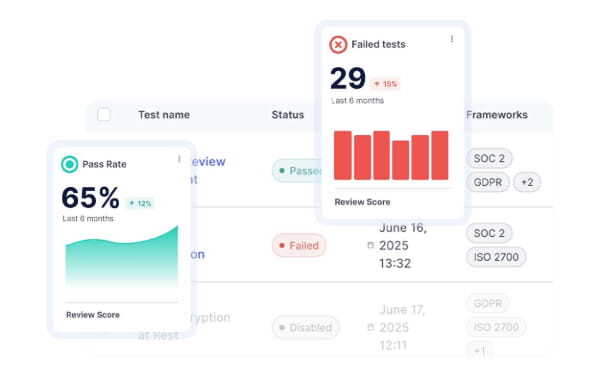
Continuous control monitoring:

Ongoing automated testing replaces annual point-in-time audits. Control failures surface immediately. Your posture is always current. SureCloud's continuous controls monitoring tests controls automatically and flags passes and failures as they occur.
sc2026_featureassets (1)

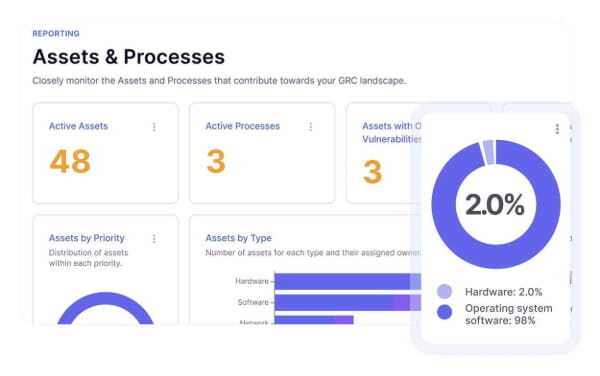
Management-ready reporting:

Provision 29 requires boards to sign off on control effectiveness. SureCloud generates defensible, evidence-backed management reports, reduced from 2 weeks to 2 days. SureCloud management reporting draws on current control and risk data, so board packs can reflect the latest position.
img-vert-fs-slider-004 (1)

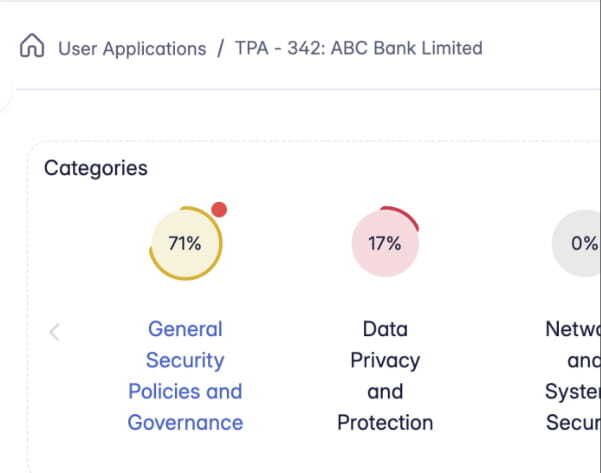
Third-party risk at scale:

DORA and FCA outsourcing requirements demand auditable vendor oversight. SureCloud TPRM covers vendor library, risk scoring, assessment workflows, and register maintenance. SureCloud applies vendor tiering, so assessment effort follows each supplier's importance and risk.
img-vert-fs-slider-005 (1)

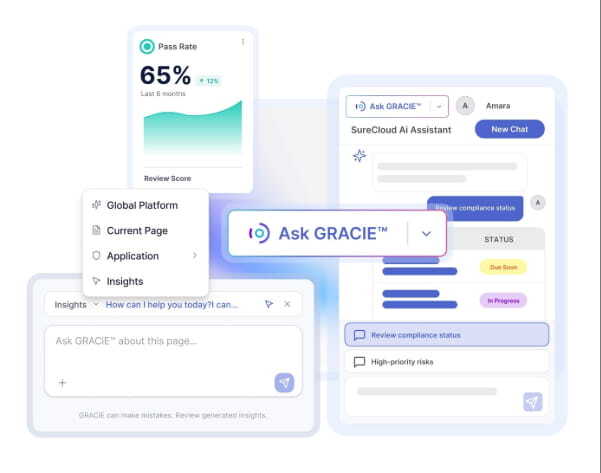
Gracie for financial services:

Cross-domain risk intelligence, automated regulatory reporting, and real-time escalation, governed end-to-end by Governance Streams. SureCloud's Gracie AI Agents with Personas and Skills perform risk and compliance activities as a virtual GRC team, and your people lead the programme.
blue-timer
40% faster decision-making with real-time risk data
blue-timer
2 Days Management report prep from 2 weeks to 2 days
blue-timer
50% faster third-party risk assessments
blue-trending
75% less effort in testing compliance and reassessment

SureCloud gives us the ability to have a wider view of all our GRC processes: TPRM, Data Privacy, and Risks in one central place. — World's largest non-bank supplier for foreign currency

SureCloud has been straightforward to implement and tailor to our framework. It's intuitive to use, so our teams have adopted it quickly. Whenever we've needed adjustments, the brilliant support team has responded promptly and actioned the changes without delay. — Mid-market UK investment management firm


gartnerdark forrester_logo idc-logo vertandix gigaom-logo-dark qks

FAQ’s

How does financial services GRC software differ from generic GRC?

The main difference is sector structure. Financial services GRC software usually arrives with DORA, operational resilience and Provision 29 requirements mapped to controls, vendor registers and board reporting. A generic GRC build usually asks the firm to assemble that structure itself. That's the mapped structure SureCloud provides, so teams spend their time producing evidence.

What are the key features of risk management software for financial services?

For risk management in financial services, it's worth looking for six capabilities: regulatory mapping to DORA, FCA operational resilience and Provision 29; continuous control monitoring; third-party risk management; continuity and incident management; board-ready reporting; and one place for operational risk management, compliance and audit. SureCloud covers these areas, with board reporting drawn from current control and risk data.

What should vendor risk management software for financial services include?

It should hold a vendor library, risk tiering, external assessments and contract records, and map them to DORA Article 28 and SS2/21. SureCloud's third-party risk management includes each of these. Tiering matters more as the supplier list grows, because that's when reviewers need to focus on the suppliers that carry the most risk.

Can SureCloud monitor risk in real time and support FCA compliance?

Yes. SureCloud's continuous controls monitoring runs automated control tests and flags failures as they're detected, so risk data stays current between audits. For FCA operational resilience, the Business Continuity & Resilience product on the Automate and Orchestrate plans holds continuity plans, scenario tests and incident records against your important business services.

Is SureCloud suitable for an Irish financial services firm?

In-scope Irish banks, insurers and investment firms are EU-authorised financial entities under DORA, and they report their Register of Information to the Central Bank of Ireland. SureCloud's DORA framework coverage, third-party risk management and continuity tools let an Irish firm run its DORA evidence from a single programme.

Does the EU Cyber Resilience Act apply to financial services firms?

Only where a firm makes a product with digital elements available on the EU market. The Cyber Resilience Act (Regulation (EU) 2024/2847) places its obligations mainly on manufacturers, importers and distributors. Manufacturer reporting under Article 14 applies from 11 September 2026; most other obligations apply from 11 December 2027.

Financial services risk management. Fully evidenced.
SureCloud's GRC platform gives financial services firms live evidence for compliance, risk and board reporting.
g2-orange
Reviews

Read Our G2 Reviews

Review us on G2

4.5 out of 5

"Excellent support team"We've been happy with the product and the support and communication has been excellent throughout the migration and onboarding process.

Posted on
G2 - SureCloud

5 out of 5

"Great customer support"

 The SureCloud team can't do enough to ensure that the software meets our organisation's requirements. 

Posted on
G2 - SureCloud

4.5 out of 5

 "Solid core product with friendly support team"

 We use SureCloud for Risk Management and Control Compliance. The core product is strong, especially in validating data as it is... 

Posted on
G2 - SureCloud

5 out of 5

 "Excellent GRC tooling and professional service"

We've been happy with the product and the support and communication has been excellent throughout the migration and onboarding process.

Posted on
G2 - SureCloud

4.5 out of 5

"Straightforward Implementation, Intuitive Use, and Brilliant Support"

SureCloud has been straightforward to implement and tailor to our framework. It’s intuitive to use, so our teams have adopted it quickly...

Posted on
G2 - SureCloud

5 out of 5

"Easy to Use, Beautiful Graphs, and a Helpful, Responsive Team"
Very easy to use and really nice graphs are created. The team are also very helpful and quick to respond

Posted on
G2 - SureCloud

DORA. FCA. Provision 29. One platform for full compliance.