gartner-reviews-dark 4.2/5 (56)

RESOURCE COLLECTION

EU Cyber Resilience Act: everything you need to know

The EU Cyber Resilience Act (CRA) sets mandatory cyber security requirements for products with digital elements sold into the EU, covering secure-by-design development, vulnerability handling, and incident reporting. It applies to manufacturers, importers and distributors, including UK organisations selling into the EU market.

CRA compliance doesn't end at the CE mark. Manufacturers must keep handling vulnerabilities, issuing updates, and reporting actively exploited flaws for as long as the product is supported - this is an ongoing obligation, not a one-off assessment. Learn more about compliance vs continuous assurance.

Not selling products into the EU? Visit the Cyber Essentials hub instead - the UK's own government-backed certification scheme, and often required for public sector contracts.


Click Here to Jump To CRA Resources

CRA-header-image (4)

Prepare for the EU Cyber Resilience Act with a more connected approach to compliance

The Cyber Resilience Act sets a baseline for cyber security across the lifecycle of any product with digital elements sold in the EU. It covers secure-by-design and secure-by-default development, vulnerability handling and coordinated disclosure, security updates, and technical documentation, all assessed through a conformity assessment appropriate to the product's risk classification - default, important, or critical.

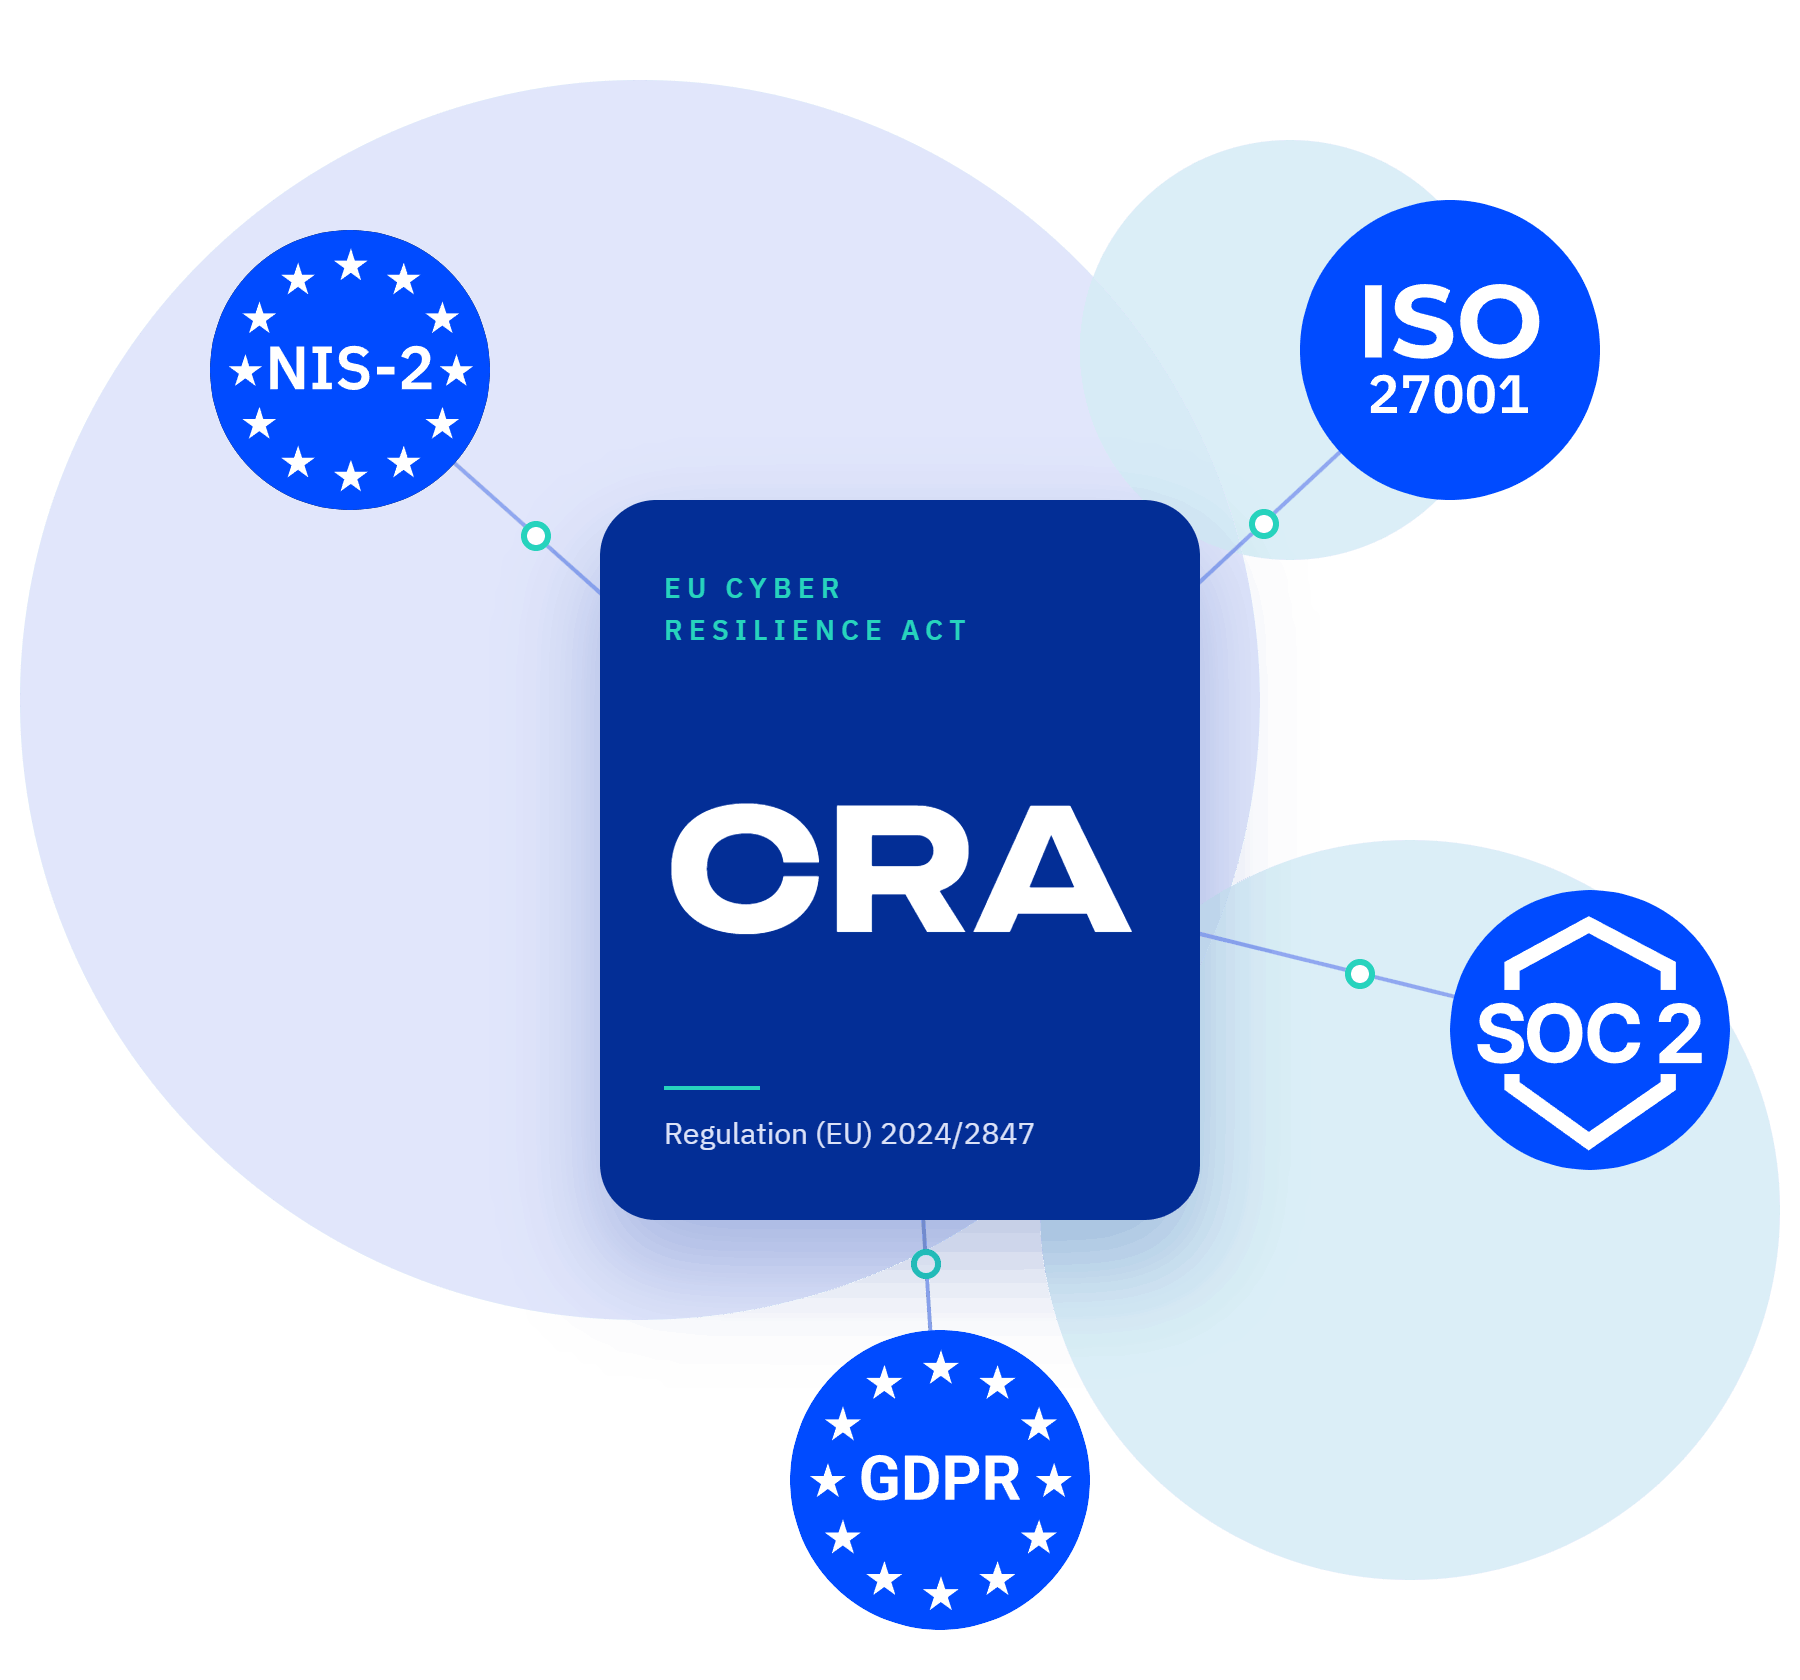
For many organisations, the challenge is not understanding that the CRA applies. It is determining exactly which products are in scope, classifying them correctly, building and maintaining a software bill of materials (SBOM), and standing up vulnerability disclosure and incident reporting processes that meet the CRA's tight reporting deadlines. This becomes even harder when CRA obligations sit alongside other requirements such as NIS 2, ISO 27001, GDPR, or existing sector-specific product rules.

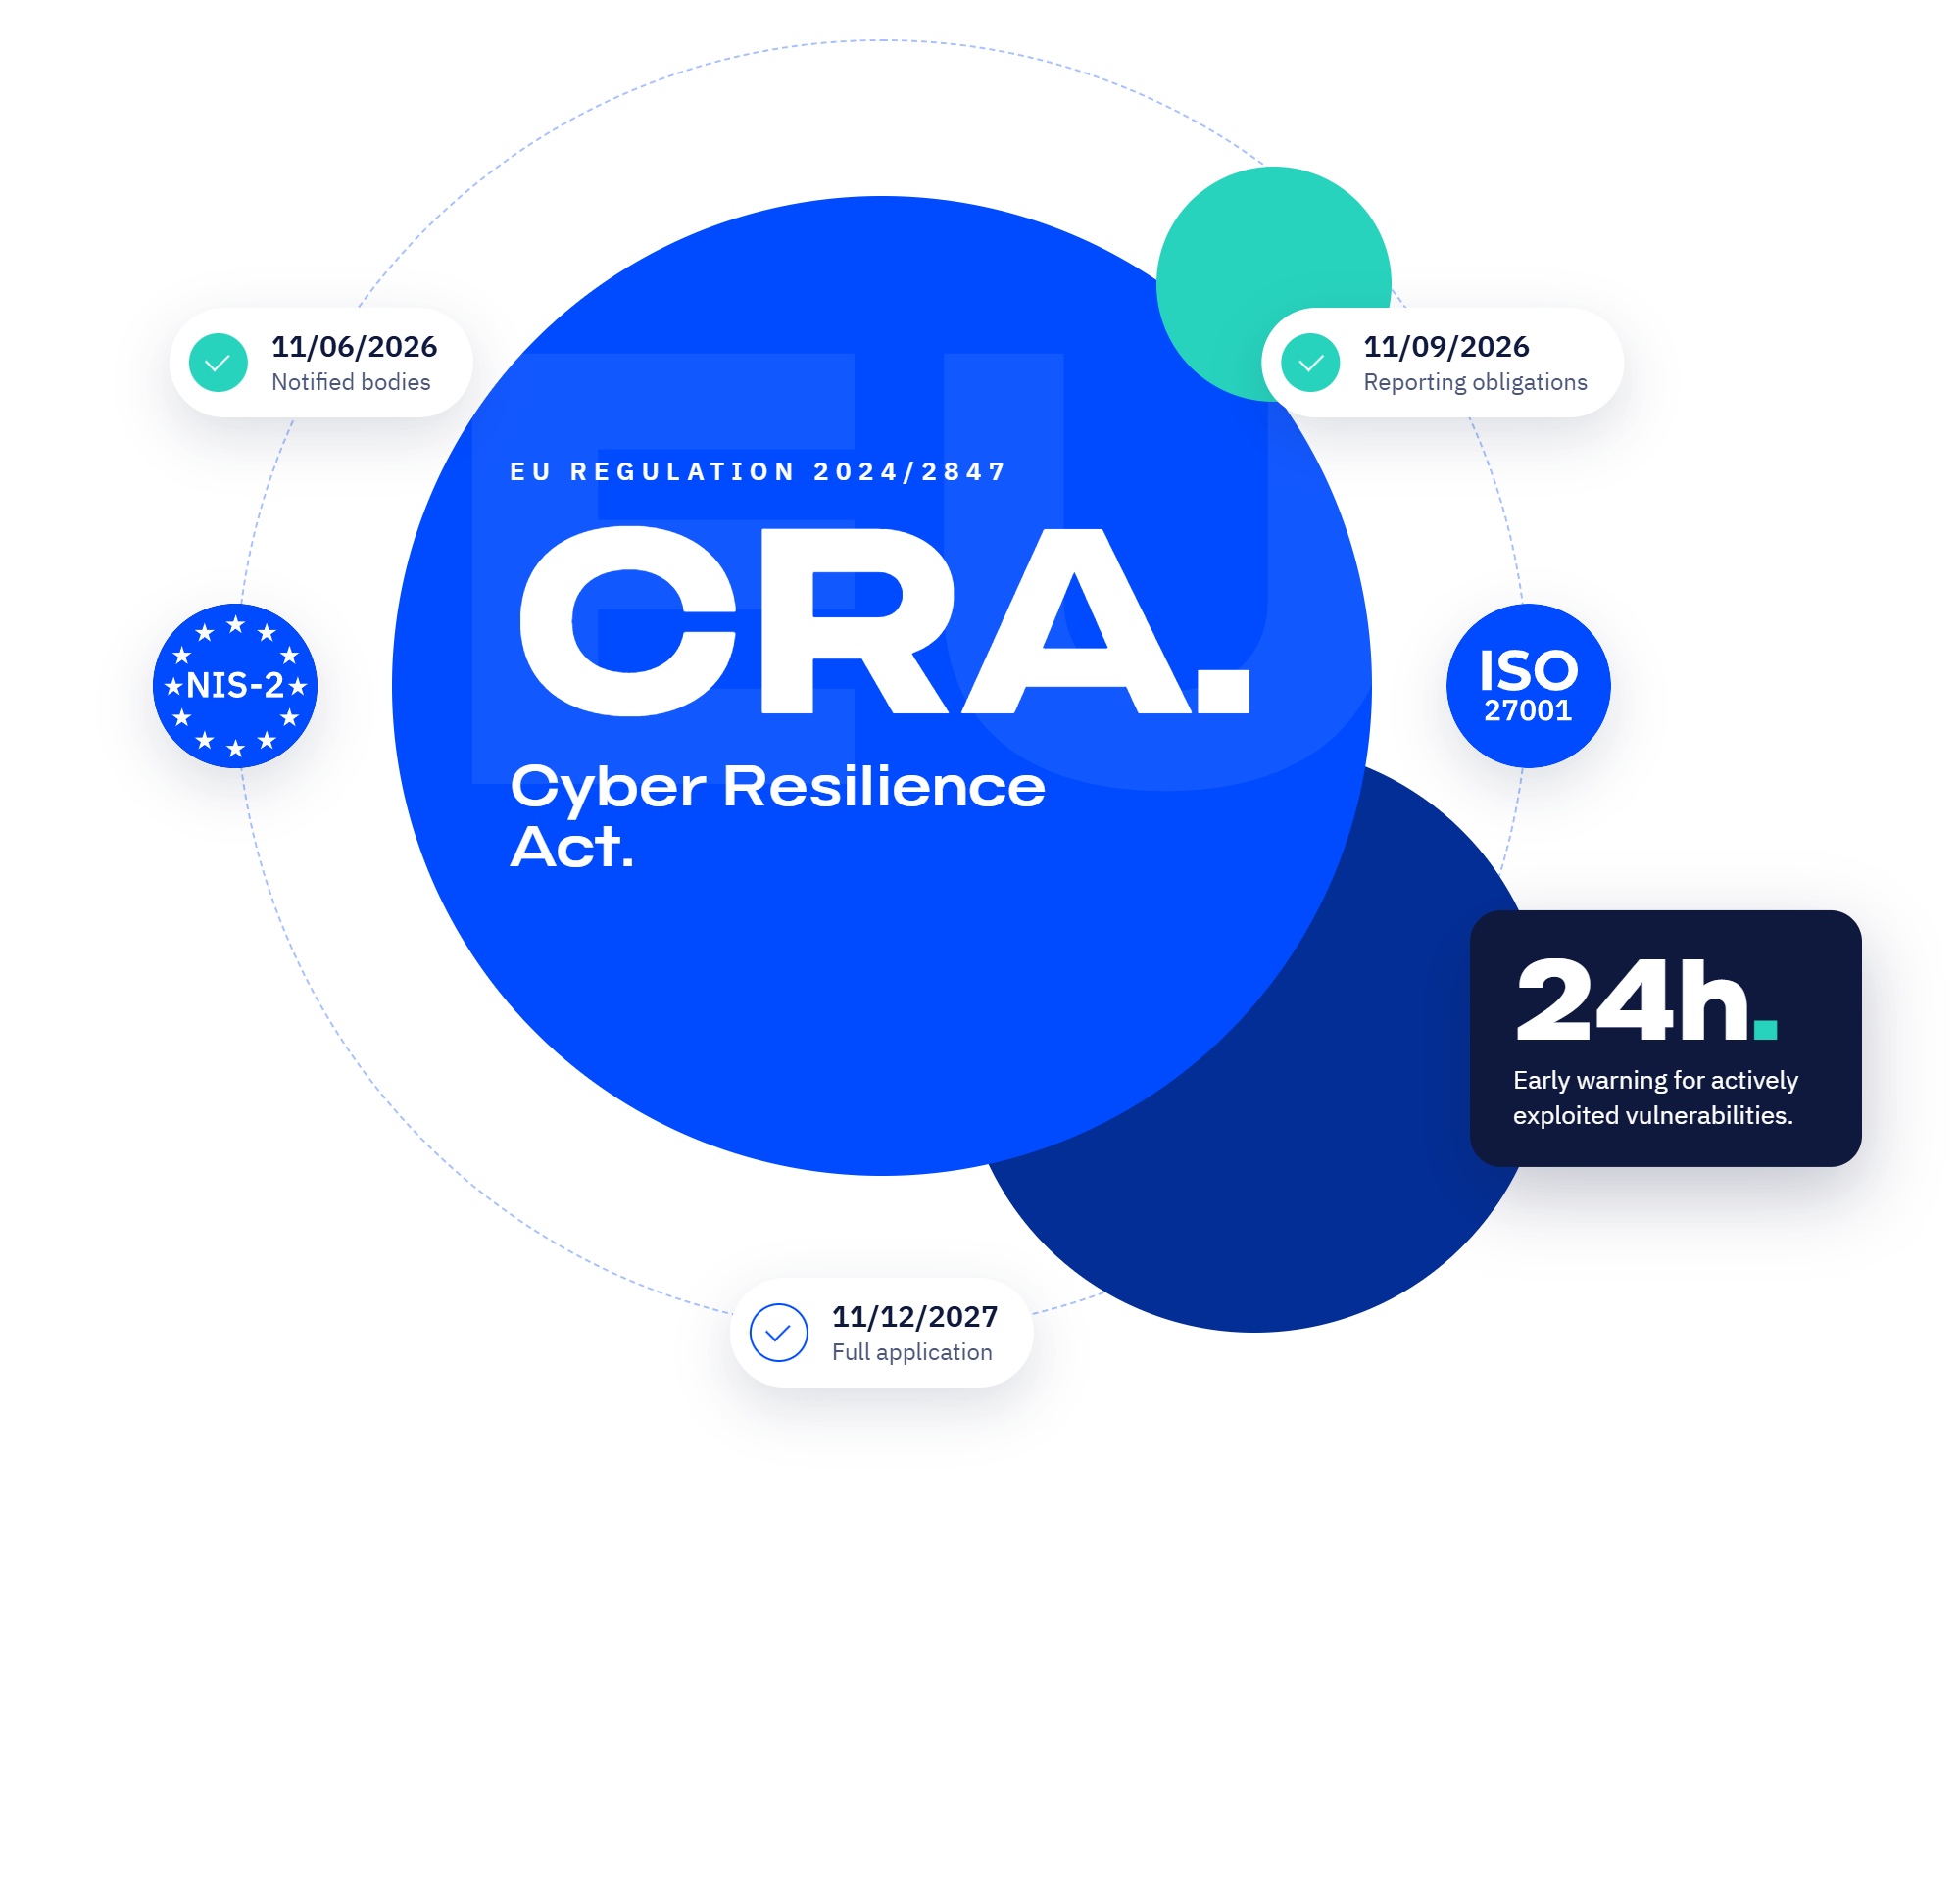
This collection gives you practical guidance on the EU Cyber Resilience Act, including what it is, which products and organisations are in scope, the key dates and deadlines to plan around, the reporting obligations that are now live, and what the CRA's SBOM requirements mean in practice.

SureCloud helps compliance and security teams manage the Cyber Resilience Act as part of a wider GRC programme. By centralising controls, evidence, assessments, policies, and remediation activity, organisations can reduce manual effort, improve visibility, and move from point-in-time certification towards continuous assurance.

CRA Related Frameworks

Explore EU Cyber Resilience Act articles

The Cyber Resilience Act touches everything from product design to post-market vulnerability reporting, and it's easy to lose track of where to begin. Start with the fundamentals below, then go deeper on scope, requirements and reporting once you know where your organisation stands. 
blue-timer
80% less audit prep time for ISO 27001 and SOC 2
blue-users
65% reduction in manual 
evidence collection
blue-timer
75% less effort in control testing compliance and reassessment
blue-users
70% less manual admin
Reduce risk, strengthen compliance and build trust. Fast.

Compare Compliance Packages

dark-icon-robot

Assure

dark-icon-automate

Automate

dark-icon-orchestrate

Orchestrate

Compliance & Policy Management
Available in base package
Product available for purchase
Control Libary & Assessment
Mapped Control Framework
ISMS Statement of Applicability
Automated Evidence Collection
Policy Management
---
Design & Operating Tests
---
---
Compliance Assessment
---
---